
Summary
A backup and disaster recovery plan in 2026 needs to do more than restore your data, it needs to hold up under an Essential Eight review, a Privacy Act obligation, or a direct question from an insurer or client. The technology hasn’t changed much, what’s expected of you around it has. This piece covers what a solid plan should include, and how to tell if yours holds up.
In This Article
I’ve had more of these conversations lately than I used to. An insurer asking a specific question about backups before they’ll renew a policy. A client sending through a due diligence form with a section on data recovery that’s more detailed than what I’m used to seeing. Both are being asked because the rules have changed.
The businesses I talk to already have some kind of backup and disaster recovery plan running. Most of those plans were written for a hardware failure or a bad storm, not for a due diligence form or a Privacy Act obligation that didn’t exist when they were put together. Since 2024, those reforms have started rolling out in stages, and insurers and clients are asking more specific questions as a result. That’s what this piece walks through, what a plan needs to cover now, and how to tell if yours already gets there.
What Should I Include in My Backup and Disaster Recovery Plan?
A solid plan backs up financial records, client files, and emails daily, includes full system and application backups so a device can be restored entirely, and builds in a way to test those backups and keep them safe from ransomware.
Most of what needs backing up is straightforward, financial records, client documents, emails, and the systems and applications that keep the business running day to day. Where plans usually fall short isn’t what’s being backed up, it’s whether anyone’s checked it works. None of what’s above has changed much in years, it’s what you’re now expected to show against it that has, and that’s covered further on.
How Often Should I Run My Backups, And What Should They Include?
Anything that changes daily, financial records, client files, emails, should be backed up daily. System files and applications should be included so you can restore a whole machine, not just recover documents.
If you had to picture losing everything on a device right now, the question worth asking is:
What would you get back?
Financial records and client documents are the obvious ones. Emails and contacts matter more than people expect, losing a year of client correspondence is its own kind of disaster. As a starting point, I’d want at least [90] days of backup history kept, enough to restore from before a problem was even noticed, not just the most recent copy.
Why Does Testing My Backup Matter as Much as Having One, And What Makes It Ransomware Resistant?
A backup that’s never been restored is not a safety net, and if ransomware can reach and delete your backup the same way it reached your live data, it was never really separate from the risk in the first place.
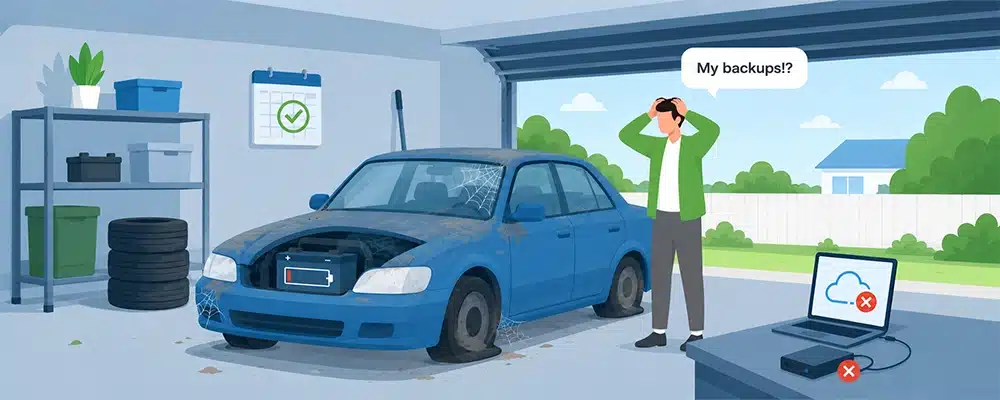
This is the part that catches people out. Having backups running is one thing. Knowing they’ll restore under pressure is another. I’ve seen businesses assume this was handled simply because it had never been questioned, right up until they needed it. It’s a bit like a car that’s been sitting in the garage for a year, you don’t know if it’ll start until you turn the key.
The other thing worth knowing is that modern ransomware doesn’t just lock your live systems, it goes looking for the backup too. If your backup sits on the same network, connected the same way your regular files are, it can be reached and deleted the same way. An offline or immutable copy, one that can’t be altered or deleted even by someone with the right login, is what protects you here.
Is My Backup and Disaster Recovery Plan Good Enough?
The honest way to know is to check whether your plan has been tested recently, whether it accounts for ransomware specifically, and whether there’s an actual written procedure, not just a backup running in the background.
3 things to ask yourself
- When did I last test my backup, not just check that it ran?
- Does my plan cover ransomware, not just hardware failure?
- Do I have a written recovery procedure someone else could follow?
If you’re not sure on any of those, it’s worth getting cyber security advisory services involved rather than guessing.
Read our article on best practices for Data Recovery & IT Disaster Planning.
What Happens If My Backup Plan Has Never Been Tested?
The difference shows up the moment things go wrong, one business restores within hours because the plan was tested, the other finds out mid-crisis that their backups didn’t cover what they thought.
Same Attack, Two Very Different Outcomes
Let’s explore two regional businesses, similar size, similar setup. Business A has a tested recovery process. Business B assumes their backups are up to date. Both businesses are hit with a ransomware attempt. Business A is back up and running within a few hours, whereas Business B has their backup sitting on the same network, so the ransomware reaches that too. Their recovery takes a week, they lose all their client files from the last year and lose 3 clients due to the downtime.
Getting your disaster recovery plan tested before anything happens is really the whole point.
The Bottom Line
Most of what goes into a backup and disaster recovery plan hasn’t changed much since 2024. What’s changed is the law behind it, Privacy Act reforms have been rolling out in stages since then, and insurers and clients are asking more specific questions as a result.
If you’ve got backups running and you’ve never tested them or checked them against what you’re now expected to show, it’s worth taking the time to find out where you stand, before someone else asks you first.
If you want a hand working through it, Future IT Services can help you check where the gaps are with managed IT services and support built around this.
Frequently Asked Questions
- Are we liable under the new 2026 Privacy Act updates?
It depends on your business and how you handle data, so I won’t pretend to answer that in two sentences. The first tranche of reforms is already in force, with more obligations around automated decision making coming in December 2026. If you’re not sure where you stand, it’s worth checking with the OAIC or a privacy lawyer directly. - Do our backups align with the Essential Eight?
Regular backups are one of the eight strategies, but alignment isn’t pass or fail, it’s measured on a maturity scale. In my experience, businesses land somewhere in the middle of that scale rather than at either end, and moving up a level is a progression, not an overnight fix. - Are we legally allowed to pay a ransomware fee to get our data back?
This isn’t a quick answer, it touches sanctions law and mandatory reporting obligations that depend heavily on the specifics. If you’re ever facing this decision, a lawyer needs to be part of that conversation. - Where is our recovered data physically hosted?
This depends entirely on your provider and the plan you’re on. If keeping data onshore in Australia matters to you, particularly with client or patient information involved, it’s worth confirming directly rather than assuming.